

Checking a password without sending it.
How zxcvbn judges a password by the patterns people use, why the page never sends it anywhere, and what a strength check cannot tell you.
By Suraj Kumar2 min read
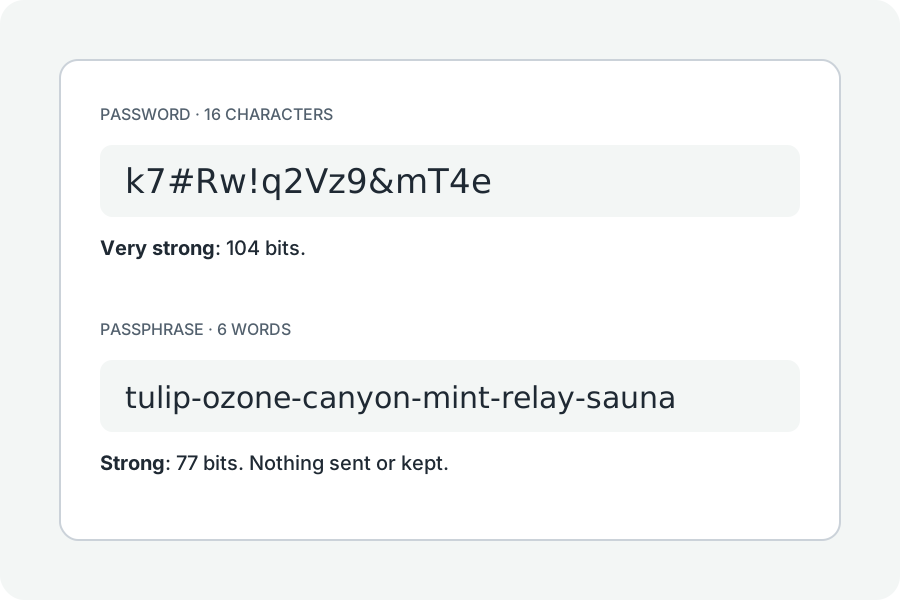
A strength check should never need your password to leave your device.
The patterns people use.
zxcvbn, made at Dropbox and described by Daniel Wheeler in 2016, looks for dictionary words, names, dates, keyboard runs, repeats and swapped letters, and estimates the guesses an attacker trying those first would need.
Nothing sent.
The page runs zxcvbn-ts in your browser; the password is never sent, kept or compared with lists of leaked passwords online.
What it cannot tell.
It cannot know whether a password was leaked or used elsewhere; a password manager's breach check can. A random password from the generator needs no check.
Further reading
Topics: password strength checker · how secure is my password · zxcvbn · password checker · password strength test
A little less theory. A little more doing.
Try it on your own terms, with a free browser tool.
Try the tool